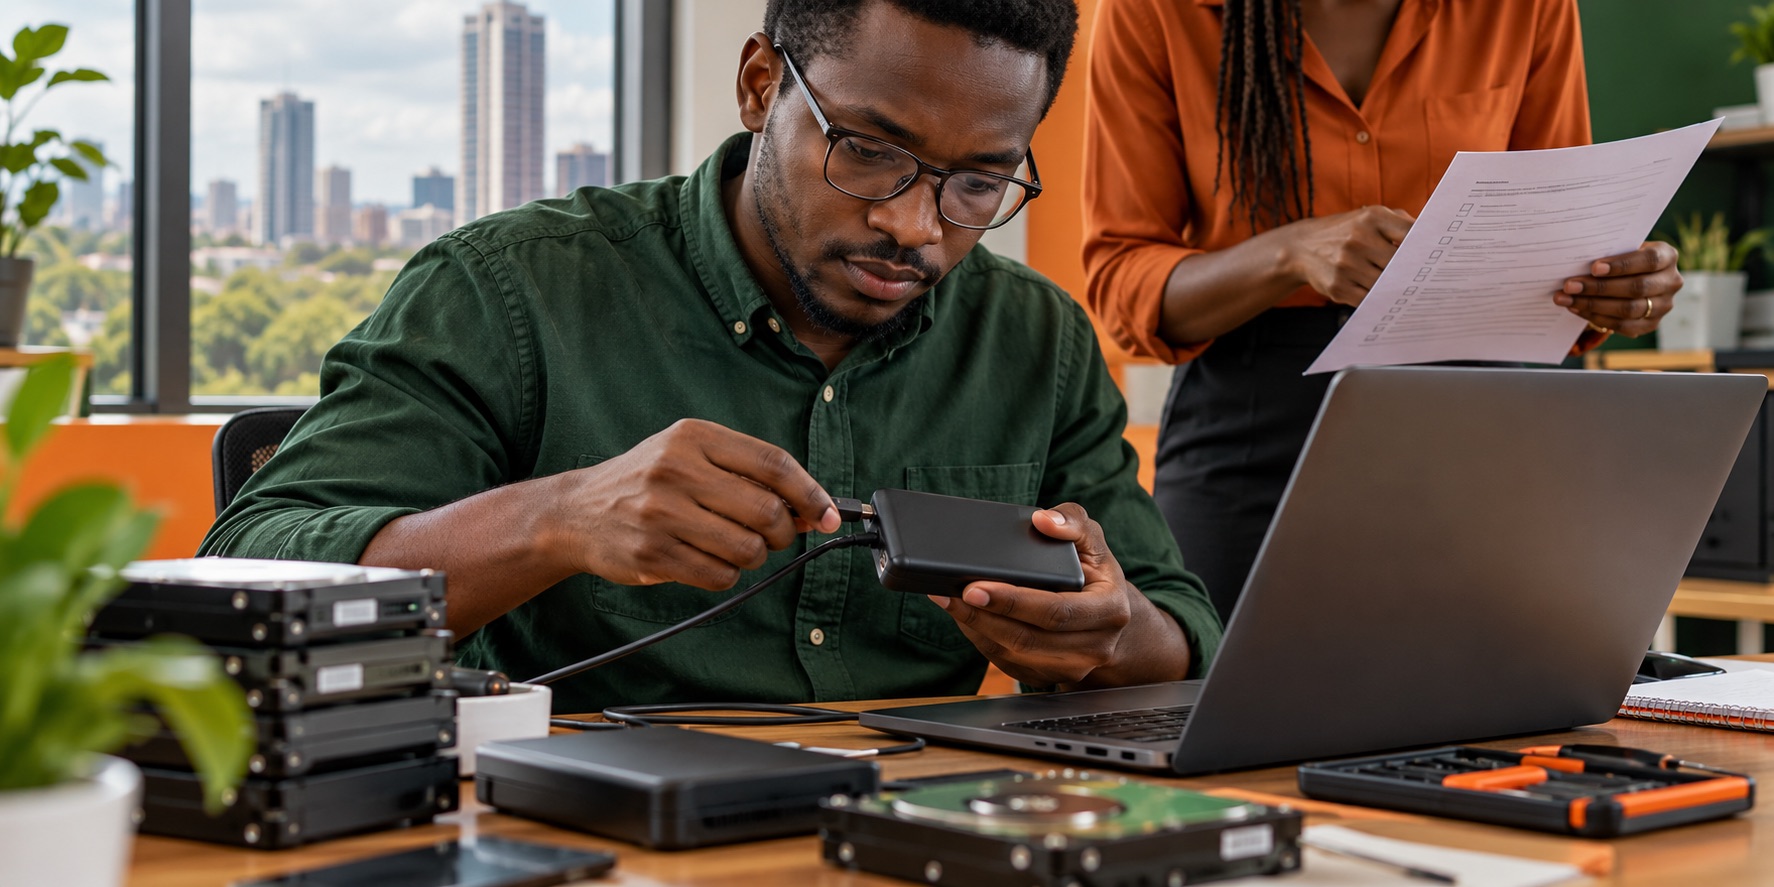
Recovery depends on whether a usable copy exists for the relevant point in time and whether the right person can request a restore.
05 / Resilience · Data Protection as a Service
Protect the information your business cannot afford to lose.A practical conversation about critical data, backup copies, restore processes and the responsibilities that support recovery.
The challenge
Make the moving parts work together.A backup is useful only if the right information is captured and a restore can be completed when needed. Recovery planning also depends on people, applications and access, not storage alone.
Who this is for
For organisations with critical business records, dependence on shared files or applications, or uncertainty about what can be restored after an incident.
Where this becomes useful
Recognisable moments. Practical responses.Business recovery may require applications, credentials, connectivity and staff coordination in addition to backed-up data. The restoration order matters.
A successful backup job does not prove that the information can be restored into a usable system. A recovery test should check both integrity and practical access.
What to explore
Practical capabilities, scoped to your environment.Each engagement starts by confirming the systems, responsibilities and coverage that apply to your organisation.
Data and system inventory
Identify information and applications that matter most to operations.
Backup design
Discuss copy locations, schedules and retention as explicit design choices.
Restore process
Define who initiates a restore and how integrity and usability are checked.
Recovery planning
Consider dependencies, communication and the sequence for bringing work back online.
A working model
From first conversation to a clearer next step.These stages show how a technology engagement can be structured. The actual delivery plan is agreed with your team.
01Identify critical data
02Create a backup plan
03Verify a copy
04Restore & review
Define the engagement
Four decisions to settle before delivery.The plan should record source systems, copy schedule, retention, restore authority, test approach and dependencies. Backup, information security, privacy governance and legal compliance remain separate areas of responsibility.
- 01Which data and systems are essential?
- 02How often should copies be made and how long kept?
- 03Where are copies held and who can access them?
- 04How will restore tests and recovery priorities be agreed?
Practical value
What better coordination makes possible.- Clearer understanding of recoverable information
- A defined path to request restoration
- Better visibility of gaps in current practices
Procurement questions
Good questions before you commit.Is backup the same as cybersecurity?
No. Backups help recover information after loss or disruption. Access controls and threat prevention address different risks and need separate design.
Does this make us compliant with privacy law?
No. Privacy governance and legal compliance require their own assessment and responsibilities. This service page makes no compliance guarantee.
How quickly can we recover?
Recovery time depends on data volume, systems, copy design and agreed process. Recovery targets should be set and tested for each environment.
Begin with what matters
Tell us what your team needs technology to make easier.